Guides
Accounts and permissions
Connect Cloudflare accounts with Sign in with Cloudflare or an API token, what each permission is for, how to fix a missing one in place, and where credentials are kept.
Quick Share needs no account. Everything on your own domains (routes, shares on your domain, Snapshots, logins, edge protection) goes through a Cloudflare account you connect once. This page covers the ways to connect, what Teitunnel asks Cloudflare for and why, and what to do when a permission is missing.
Connect an account
Open Settings ▸ Accounts and choose Connect an Account. Before any account is connected, the Overview's Use My Own Domain… opens the same sheet.
There are three ways to connect:
Choose Sign in with Cloudflare
Your browser opens Cloudflare's sign-in and consent page. The sheet says Waiting for you to finish in your browser… and shows the sign-in link to copy, in case the browser didn't open or you want to use another one.
Allow access
Review what Teitunnel asks for (see the consent screen) and allow it. The browser tab says You're signed in, and you can close it.
Done
Back in Teitunnel, every account the sign-in reaches is connected. Cancel Sign-In stops waiting; the sign-in also gives up by itself after 5 minutes.
Nothing to copy or paste, and the sign-in lasts: Teitunnel keeps a refresh token and gets new short-lived access tokens by itself.
Which one to use
| Sign in with Cloudflare | API token | cloudflared login | |
|---|---|---|---|
| Setup | One click and a consent screen | Create, copy, paste | Already done, if you used cloudflared |
| Domains | Every domain the sign-in reaches | Every domain, or the ones you choose | One |
| Add a permission later | Connect with an API token that has it | Edit the token in the dashboard, nothing to paste | Connect with a sign-in or token |
| On a server or in CI | No (needs a browser) | Yes, from the environment | No |
| Shown in Settings as | Signed in with Cloudflare | API token | cloudflared login · one domain only |
On a desktop, Sign in with Cloudflare is the quickest. Use an API token when you want to limit what Teitunnel can reach, on servers and in containers (Servers and containers), and in CI.
The consent screen
Sign in with Cloudflare asks for everything Teitunnel can do in one consent, so you don't
come back for each feature. Four scopes are required; without them Teitunnel can't
put anything on your domains. offline_access keeps you signed in. The rest are
optional: you can decline any of them on the consent screen, and Teitunnel keeps
working without the features they belong to. When you later use one of those features,
Teitunnel shows what's missing and how to add it, in place (see
When a permission is missing).
| Scope | Required | What Teitunnel does with it |
|---|---|---|
argotunnel.write | Yes | Create and run tunnels, their routes and connector logs |
dns.write | Yes | Add, change and remove the DNS records of your routes |
zone.read | Yes | List your domains |
account-settings.read | Yes | Find your accounts and their names |
offline_access | To stay signed in | A refresh token, so the sign-in lasts |
access-app.write, access-policy.write, access-acct.write, zone-access.write | No | Require a login in front of a route, and add the one-time code login method |
zone-waf.write, zone-transform-rules.write | No | Edge protection: bot and rate limit rules, header rules |
access-service-token.write | No | Service tokens for machines |
workers-scripts.write, workers-routes.write | No | Snapshots, the offline page and the webhook inbox |
d1.write | No | Comments on Snapshots, and webhook inbox storage |
analytics.read, account-analytics.read | No | Traffic charts from Cloudflare's edge |
teams-networks.write, teams.read | No | Private networks, and the Doctor's WARP checks (read only) |
load-balancers.write, load-balancing-monitors-and-pools.write | No | Load balancing across machines |
offline_access is how Cloudflare hands out a refresh token. If it's refused, Teitunnel
says Cloudflare didn't allow offline access and the sign-in doesn't complete.
Every permission, and what needs it
API tokens use the dashboard's permission names. The link behind Open Cloudflare selects everything in the first part of this table; the last rows are added by hand if you use those features.
| Dashboard permission | OAuth scope | Needed for | In the token link |
|---|---|---|---|
| Account · Cloudflare Tunnel · Edit | argotunnel.write | Tunnels, routes, private network ranges, connector logs | Yes |
| Zone · DNS · Edit | dns.write | Routes' DNS records, shares on your domain, reservations | Yes |
| Zone · Zone · Read | zone.read | Listing your domains | Yes |
| Account · Account Settings · Read | account-settings.read | Naming the account | Yes |
| Account · Access: Apps and Policies · Edit | access-app.write, access-policy.write, zone-access.write | Logins in front of routes, shares and Snapshots | Yes |
| Account · Access: Organizations, Identity Providers, and Groups · Edit | access-acct.write | Adding the one-time code login method when the account has none | Yes |
| Account · Access: Service Tokens · Edit | access-service-token.write | Service tokens | Yes |
| Zone · Zone WAF · Edit | zone-waf.write | Bot, AI crawler and rate limit rules for one hostname | Yes |
| Zone · Transform Rules · Edit | zone-transform-rules.write | Header rules for one hostname | Yes |
| Account · Workers Scripts · Edit | workers-scripts.write | Snapshots, offline page, webhook inbox | Yes |
| Zone · Workers Routes · Edit | workers-routes.write | A Snapshot's hostname, and the offline page and inbox in front of a route | Yes |
| Account · D1 · Edit | d1.write | Snapshot comments and webhook inboxes (one database, teitunnel-data) | Yes |
| Zone · Analytics · Read | analytics.read | Each route's traffic from Cloudflare's edge | Yes |
| Account · Account Analytics · Read | account-analytics.read | Traffic numbers Cloudflare keeps per account | Yes |
| Account · Load Balancing: Monitors and Pools · Edit | load-balancing-monitors-and-pools.write | Load balancing (a paid Cloudflare add-on) | No |
| Zone · Load Balancers · Edit | load-balancers.write | Load balancing | No |
Only the first four are needed for routes. Everything else is optional: without it, the
feature says what's missing when you open it, and the rest keeps working. With an API
token, Cloudflare Tunnel · Edit also covers private networks; a sign-in asks for them
separately (teams-networks.write, and teams.read for the Doctor's WARP checks). The
same list, with the token link's keys, is in Permissions and scopes.
See what an account can do
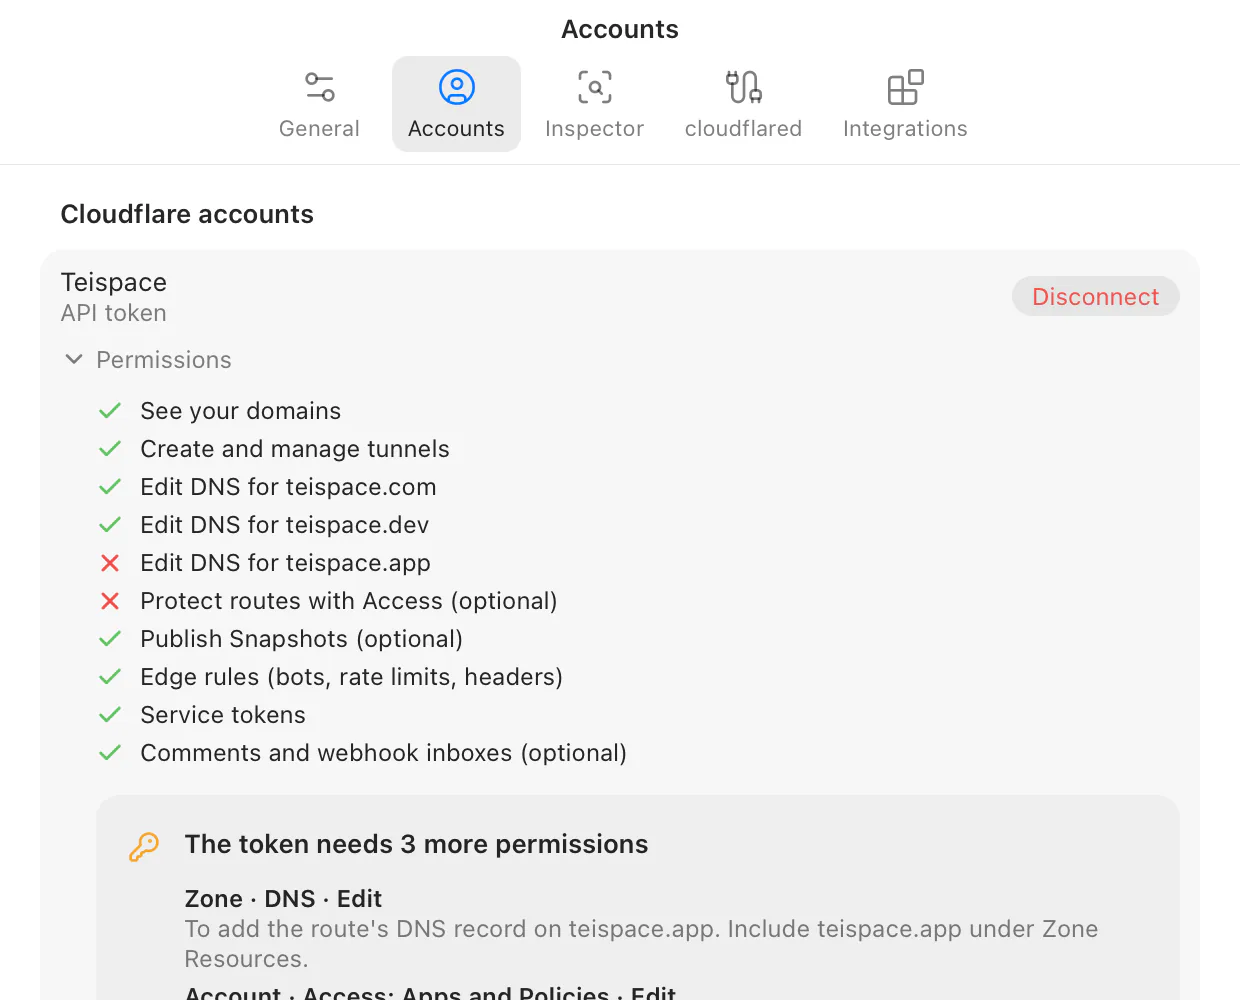
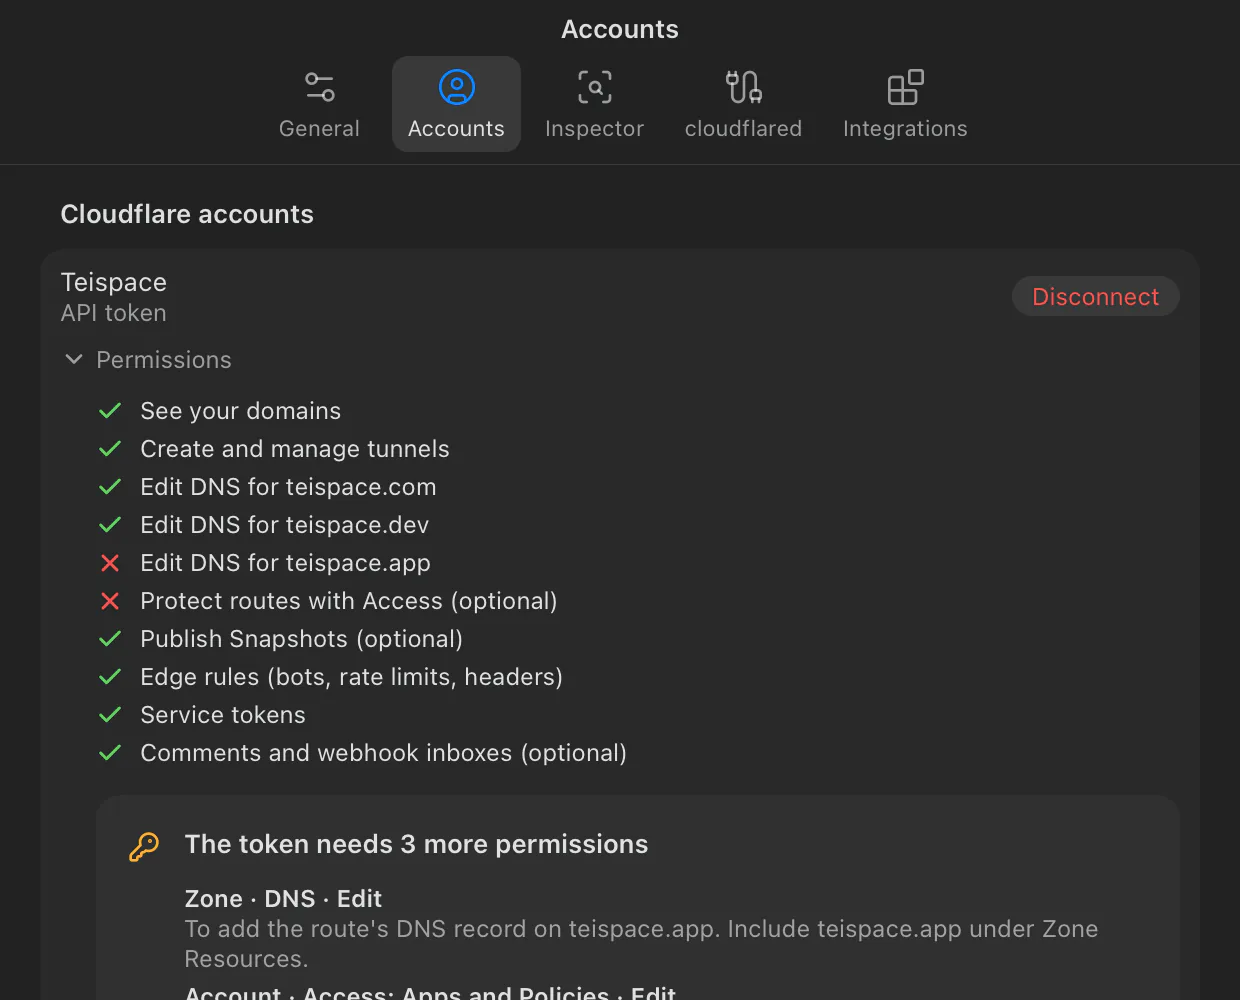
In Settings ▸ Accounts, open Permissions under an account. Teitunnel checks with Cloudflare, without changing anything, and lists:
| Row | What it checks |
|---|---|
| See your domains | Zone · Zone · Read |
| Create and manage tunnels | Account · Cloudflare Tunnel · Edit |
| Edit DNS for domain | Zone · DNS · Edit, one row per domain |
| Protect routes with Access (optional) | Both Access permissions for logins |
| Publish Snapshots (optional) | Account · Workers Scripts · Edit |
| Edge rules (bots, rate limits, headers) | Zone WAF and Transform Rules, both needed |
| Service tokens | Account · Access: Service Tokens · Edit |
| Comments and webhook inboxes (optional) | Account · D1 · Edit |
Each row is Allowed (a check mark), Not allowed (a cross), Unknown (a dash: Cloudflare couldn't be asked just now, for example offline) or Needs Cloudflare Zero Trust, which isn't set up yet. Domains' own permissions are also shown in Domains, per domain.
When a permission is missing
Teitunnel doesn't stop at an error. Wherever a feature needs something the account's credential lacks (a route's login, the Doctor, Snapshots, protection, this Permissions list), it shows a card, The token needs one more permission, listing each missing permission by its dashboard name and why it's needed.
For an API token, the token keeps its value, so nothing is pasted:
Open API Tokens
It opens your tokens in the Cloudflare dashboard.
Edit the token
Choose Edit next to the token you connected (it's named Teitunnel if you used the link). Add the permissions from the card, and check that this account and your domains are included under the resources.
Update it
Choose Continue to Summary, then Update Token, and switch back to Teitunnel.
Teitunnel checks again when its window becomes active (or choose Check Again) and carries on where you were; a change you were reviewing is planned again. If something is still missing, the card says so.
Or choose Use a New Token Instead: Create Token opens the dashboard with every permission selected, and the token you paste replaces the account's credential.
For an account connected with Sign in with Cloudflare or a cloudflared login, the permissions of that login can't be edited. The card offers to connect the account with an API token that has them (Create Token, then paste it); it replaces the current credential, and everything you set up stays.
Set up Cloudflare Zero Trust
Logins and service tokens use Cloudflare Zero Trust (Access). An account that has never used Zero Trust has the permissions but nothing to use them on yet, so instead of a permission card Teitunnel shows Set up Cloudflare Zero Trust:
- Open Zero Trust and choose a team name.
- Pick the Free plan when asked (free for up to 50 users), then come back.
Only the dashboard can do this step. Teitunnel checks again when you come back (or choose Try Again) and carries on. Adding a domain to Cloudflare works the same way: Add a Domain to Cloudflare opens the dashboard's page for it.
Several accounts
One sign-in or token can reach several Cloudflare accounts; each one it reaches is connected, and you can connect more with Connect an Account. With more than one connected:
- Routes, Domains, Tunnels, Analytics and Activity have an Account menu in the toolbar. The account you pick is remembered; if it's disconnected, the first account is shown.
- Quick Share's Address menu lists your domains, so a share can go on any of them.
- On the command line, commands that work on one account take
--accountwith the account's name or id. It's needed only when several are connected.
Disconnect an account
In Settings ▸ Accounts, choose Disconnect next to the account and confirm. Teitunnel:
- stops this computer's connectors for the account and ends temporary shares on its domains (their routes and records are removed while the credential still works);
- revokes the sign-in with Cloudflare, for accounts connected with Sign in with Cloudflare;
- deletes the account's credentials from your keychain;
- deletes what it remembered about the account on this computer (activity, ownership notes, Snapshots list, schedules and the like).
Its tunnels, routes and DNS records stay in Cloudflare, offline until a connector runs them again. To remove them too, remove the routes first. An API token isn't deleted from Cloudflare: delete it in the dashboard's API Tokens if you no longer need it.
Where credentials are kept
Credentials are kept only in your system's credential store: the keychain on macOS,
Windows Credential Manager on Windows, and the Secret Service (GNOME Keyring or
KWallet, installed and unlocked) on Linux. They're stored under the service
com.teispace.teitunnel:
| Item | What it holds |
|---|---|
cf:<account-id>:apiToken | An API token |
cf:<sign-in>:oauth | The refresh token of a Cloudflare sign-in, shared by every account it reaches |
cf:<sign-in>:oauth-access | The current access token of that sign-in, shared (see below) |
cf:<account-id>:certPem | The login copied from a cert.pem |
An API token that reaches several accounts is stored once per account, so each account can be disconnected on its own. A Cloudflare sign-in is stored once for all the accounts it reaches (older versions kept an item per account, under its id), and it's revoked when the last of them is disconnected. The database only holds each account's id, name and how it was connected. Credentials are only ever sent to Cloudflare, and never reach the app's window, logs or AI agents. See Security.
Cloudflare gives a sign-in a new refresh token every time it's used, and ends the sign-in
if an old one is used again. So the accounts a sign-in reaches share one refresh token, and
the app, the teitunnel command and the MCP server for AI agents share one access token
through the keychain; only one of them refreshes it at a time.
If Cloudflare ends a sign-in anyway (you revoked it in the dashboard, or it wasn't used for a long time), its accounts show Signed out in Settings → Accounts with Sign In Again. Teitunnel stops asking Cloudflare until you do.
From the terminal
The teitunnel command uses the accounts connected in the app, including sign-ins.
teitunnel accounts            # connected accounts: name and id
teitunnel accounts --json     # [{"id": …, "name": …}]
teitunnel setup               # connect an account with an API token (asks for it)
teitunnel routes --account Teispace
teitunnel setup asks for an API token (with Cloudflare Tunnel · Edit, DNS · Edit and
Zone · Read at least) and stores it in the keychain like the app does. Signing in with
Cloudflare is only in the app, since it needs a browser.
On a server or in a container without a keychain, don't store a token: set
CLOUDFLARE_API_TOKEN (or TEITUNNEL_API_TOKEN) for each command, or
CLOUDFLARE_API_TOKEN_FILE naming a file that holds it, as Docker secrets do. It's used
for that command only and never written to disk. With it set, teitunnel setup only checks
that it works. See Servers and containers.
Troubleshooting
- Cloudflare didn't accept this token. Check that you copied all of it and that it hasn't expired or been deleted in the dashboard.
- This token can't access any Cloudflare account or domain. It was created without resources. Create it from Open Cloudflare so all accounts and domains are selected.
- Couldn't start sign-in: ports … are all in use. The sign-in listens on this computer on port 53682, 53683 or 53684. Close other sign-in windows and try again.
- Sign-in timed out. You have 5 minutes to finish in the browser. Try again.
- Invalid access token (9109). See Troubleshooting.
- The keychain couldn't be used. Unlock it and try again. On Linux, install and unlock a Secret Service provider such as GNOME Keyring or KWallet.
Related
Last updated on
Teitunnel and Cloudflare's own tools
How Teitunnel compares with managing Cloudflare Tunnel through the cloudflared command line or the Cloudflare dashboard, and when to use which.
Import an existing setup
Move the routes of a cloudflared config.yml (a locally-managed tunnel) onto Teitunnel: where it looks, what can be imported, the plan you review, what happens to the old tunnel and its DNS records, and how to switch back.